Analysis
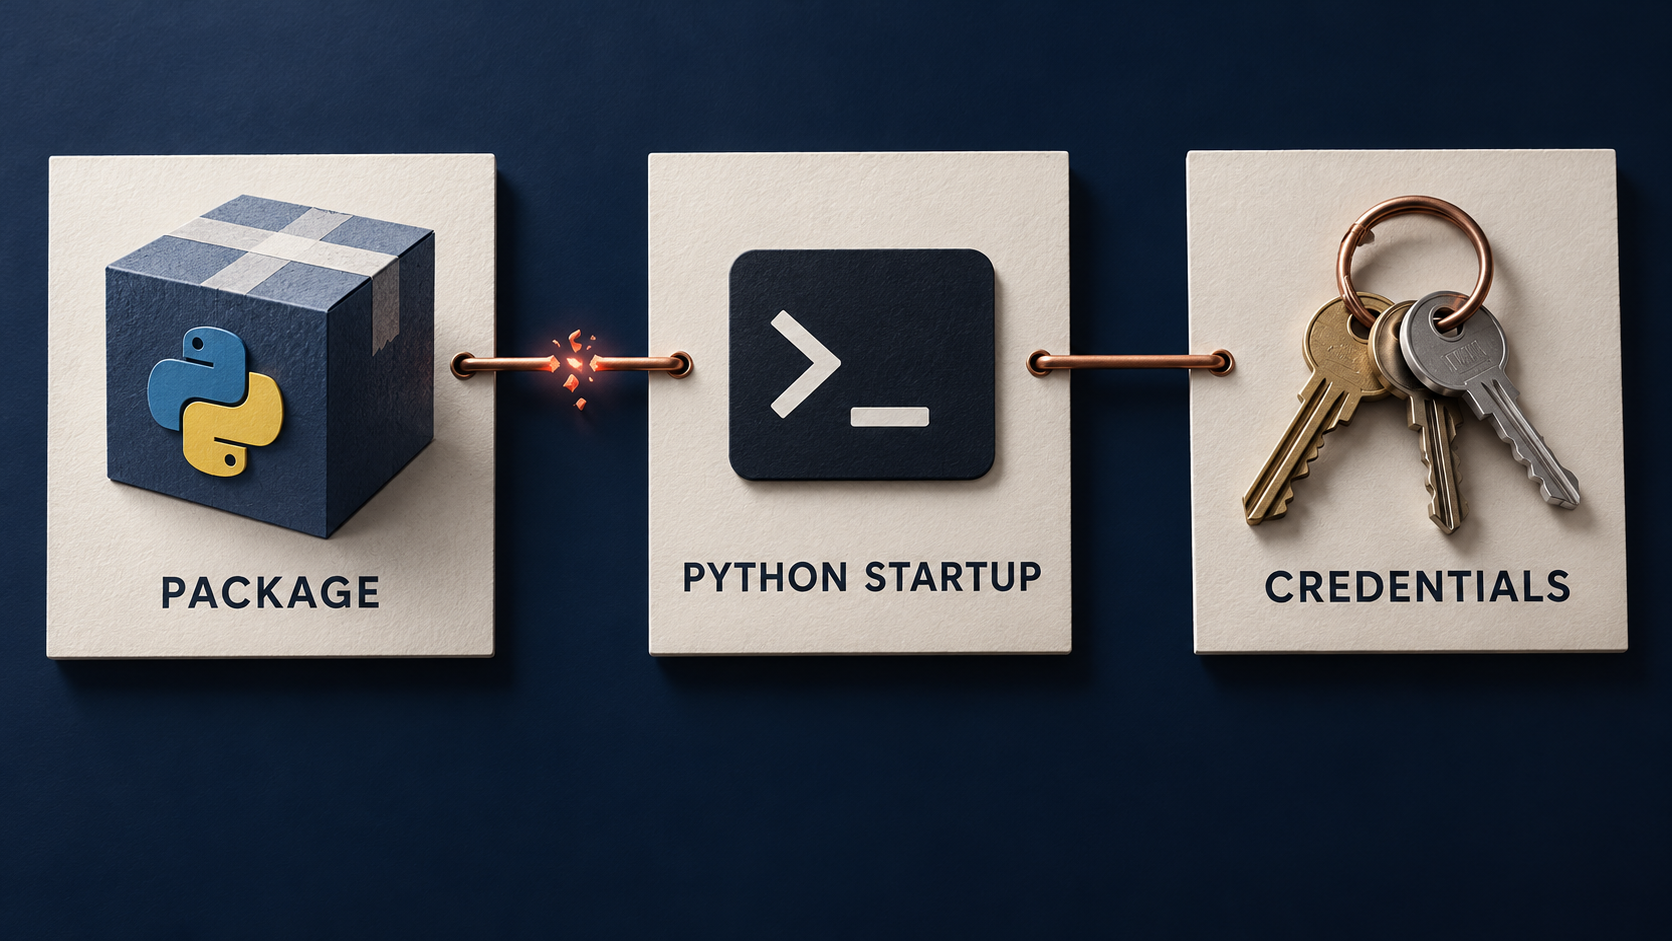
Microsoft's October 23 investigation says a compromised LiteLLM 1.107.0 release reached PyPI and official container images on October 21. Malicious startup files could execute during Python initialization, so an application did not need to import LiteLLM to activate the collector.
The researchers describe credential collection spanning developer tools, cloud environments and infrastructure. They report matching endpoint behavior on Windows and macOS, including activation during an unrelated dependency installation. Microsoft cautions against launching Python or pip inside a suspect environment merely to inspect it.
Our reading: package removal is only part of incident recovery. The report calls for addressing the affected environment, surviving processes and credentials available to the compromised identity. This edition establishes no exposure in Silver Owl systems.
Source: Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks · 2026-10-23
Why it matters
Assess startup behavior and credential reach when investigating a compromised dependency.